Insights
AI Doesn't Invent New Attacks. It Runs the Old Ones Faster.
 Dave Goldberg · 7 min read
Thinking you need a new AI threat program? First check these seven basics that the machines are already hunting.
Somewhere in the last year, “what's our AI risk?” became a board question. I'm sure your vendors have an answer ready. “It's a new class of threat which needs a new product category to match.” But I'd say for most organizations, it's the wrong question to ask and there's data to prove it.
My latest analysis of the 2026 Verizon DBIR looks at how attackers actually use generative AI. In partnership with Anthropic, Verizon analyzed 793 threat actors whose accounts were investigated for policy violations by Anthropic between March 2025 and February 2026. They investigated how much AI these bad actors were using. The conclusion was they use it a lot. The median threat actor researched or used AI assistance across 15 different attack techniques, some as many as 40 or 50. Almost all of that AI-assisted tooling mapped to well-known, well-documented attack techniques. Essentially, they were using AI on the same tried-and-true attack vectors, with less than 2.5% involving anything resembling a novel technique.
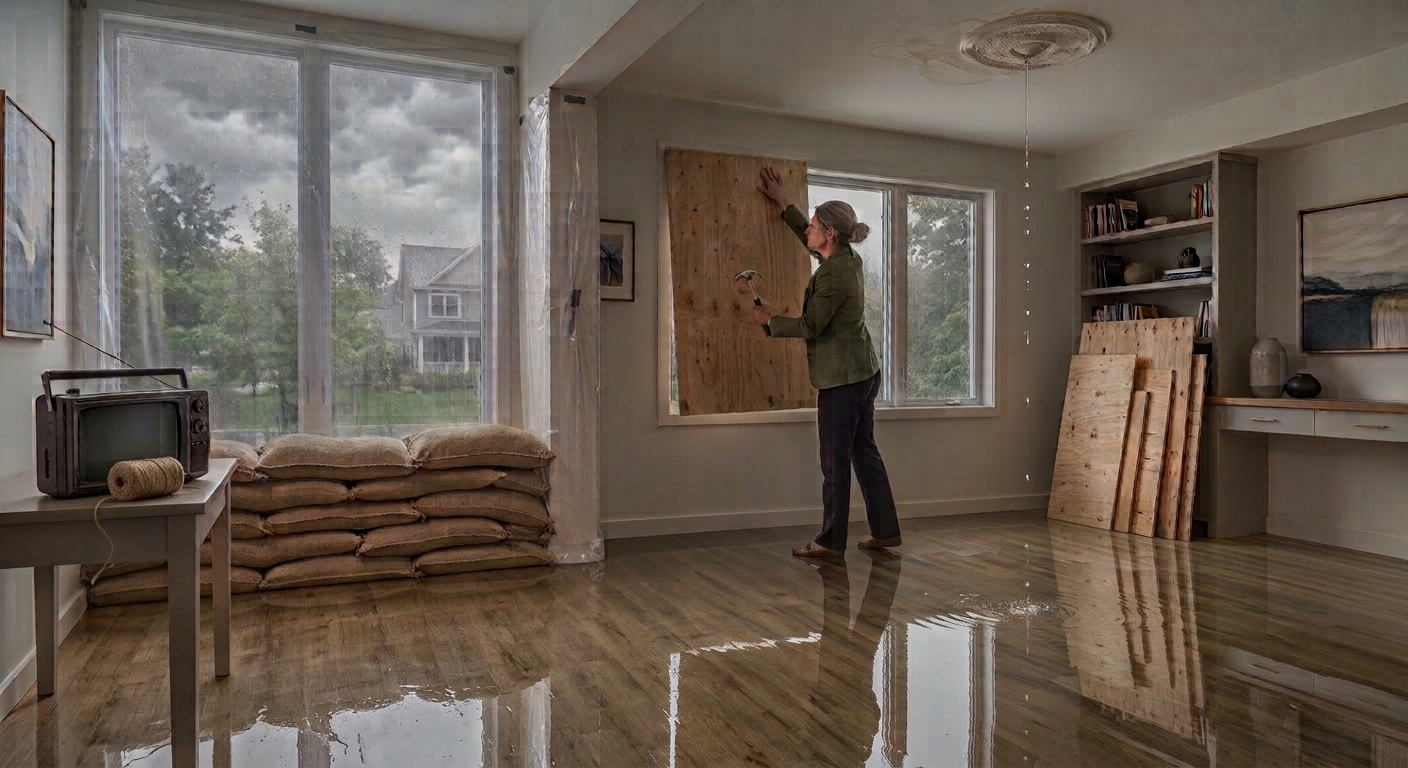
The machines are not inventing new ways in. They're running the oldest plays in the book, faster, cheaper, and at scale. Worrying about exotic AI attacks while your fundamentals have gaps is preparing for the storm of the century while the roof leaks in ordinary rain. It's the ordinary rain that's in the forecast all the time.
What acceleration actually changes
The answer is time. Reconnaissance that took an attacker weeks now takes hours. Phishing that used to arrive with typos now arrives fluent, and in your supplier's tone, with personal details about the recipient. Credential stuffing runs at machine scale. The development of exploits compresses.
The basic gaps
Don't worry about the new exotic categories of exploits. Fix the old ones. AI is shortening the time between a gap existing in your environment and someone finding it. Which means the return on fixing the ordinary gaps just went up, not down. In my typical fashion, here are the seven gaps that decide whether AI-accelerated attacks are potentially a problem for you. I've listed them in the order most likely for attackers to check them.
1. IAM policies that are over-permissioned or not enforced
“Least privilege” as defined in your policies is only as good as its enforcement. In practice, roles accumulate permissions. Well-intentioned admins configure exceptions which they forget to remove. Service accounts outlive their projects and leavers can keep access for weeks or months after they are gone. When an attacker exploits a valid account, your access policies are the only thing deciding what happens next.
AI accelerates the landing with automated phishing producing more compromised accounts per week. But the blast radius of each compromise is set entirely by you. An account that can reach everything makes a cheap compromise expensive. Access reviews are boring. But the alternative is explaining why a marketing login could touch the finance system.
2. Poor password management
Hard to believe we're still talking about this. But it remains a valid attack which is simple to defend against. Use a password manager. Require unique credentials. Establish MFA on everything that faces the internet. Change any default passwords. Don't allow shared accounts.
The reason this is urgent now is that password abuse is the single most automatable attack there is, and automation is the thing AI basically made free. The DBIR also shows why relying on humans as the defense is getting harder. Voice and text phishing convert 40% more than email phishing, with pretexting growing as a way into ransomware. You will not train people to recognize personalized deception 100% of the time, but you can make the stolen password worth less.
3. Scattered or incomplete logs
When an incident happens, the first question is what did it touch. You should be able to answer that from your logs. If they're scattered across systems, retained for a week, or never enabled, the investigation stalls inside the critical 72-hour window in which you're expected to report what happened.
The attacker's speed makes this worse. A faster intrusion means a shorter window between first foothold and real damage. How can you detect what you're not recording? Centralized logging is unglamorous plumbing. It's also the difference between having an answer and a lot of unanswered questions.
4. Poor alert processes
“I have alerts!” Sure, but do you have owners? Or triage rules? Or a definition of when something gets escalated versus de-prioritized? An unowned alert queue is essentially a lottery on whether something gets noticed. Now with AI the attack volume gets raised. Add the noise of more tooling and your lottery odds keep getting worse.
The fix is process, not another product. Someone needs to own the queue. Noisy rules get tuned. Each escalation type has a path and an SLA. If a critical alert fired at 2 a.m. tonight you should be able to name who sees it and what actions they perform.
5. Long-lived exceptions
They are the holes in your cybersecurity armor. Every environment has them. The legacy app excused from MFA. The firewall rule added during a migration with a note that says “temporary.” The vendor account that bypasses the proxy because of a software bug. Exceptions are where your controls aren't enforced. An exception without a review date is not temporary, it's permanent, undocumented and unnoticed.
AI's faster, broader reconnaissance is specifically good at finding the open door. A quarterly review of the exception list is an afternoon well spent. It's probably the highest return on investment on this list.
6. Systems not hardened
Default configurations. Unnecessary services left running. Management interfaces exposed to the internet. Edge devices running old firmware. This is unfortunately the reality on many front lines. Exploited vulnerabilities now open 31% of breaches. In today's world, AI-assisted exploit development shortens the gap between a flaw being published and being weaponized to hours, not days or weeks.
A good hardening practice gives the automated scan nothing to find. Turn off what you don't use. Take admin interfaces off the internet. Patch the edge first. None of it requires a new AI strategy, but all of it weakens an AI-assisted attacker.
7. Shadow IT, which now means shadow AI
The clearest AI risk in this year's DBIR data isn't attackers at all. It's your people. The report found 67% of users accessing AI services through non-corporate accounts from their corporate devices. With 45% of employees now using AI regularly at work, shadow AI is now the third most common insider policy violation in data loss monitoring. The top data type pasted into external models was source code. Company research and technical documentation show up too.
This is not a futuristic threat. It is asset management and data governance, the oldest disciplines there are, with a new twist. You cannot govern tools you cannot see, so policy and detection both need to be in place.
The right order
None of the above says ignore AI. It's saying AI enters your risk picture as an accelerant with more attempts and better lures in shorter timelines on attack paths that already exist. Which removes the mystery of the attack and provides clear guidance on how to prevent it.
That's how Cordaata treats it. Your risk gets evaluated against your actual environment. AI acceleration shows up where it belongs, as a shift in likelihood on paths you already have. What we help you understand is the question that really matters. Which of the seven gaps, if addressed, removes the most expected loss for you. Sometimes the AI-era priority turns out to be a password manager and an exception review. The numbers don't care that it isn't exciting.
Fix the roof before the storm of the century. It's the same roof either way.
If the board is asking about AI risk and you'd like to answer with more confidence, we should talk.